

Paper Menu >>
Journal Menu >>
 Int. J. Communications, Network and System Sciences, 2011, 4, 507-513 doi:10.4236/ijcns.2011.48062 Published Online August 2011 (http://www.SciRP.org/journal/ijcns) Copyright © 2011 SciRes. IJCNS A Two Step Secure Spectrum Sensing Algorithm Using Fuzzy Logic for Cognitive Radio Networks Ehsan MoeenTaghavi, Bahman Abolhassani School of Electrical Engineering, Iran University of Scien c e and Technology (IUST), Tehran, Iran E-mail: [email protected], [email protected] Received June 5, 2011; revised July 9, 2011; accepted July 18, 2011 Abstract In this paper, a two step secure spectrum sensing algorithm is proposed for cognitive radio networks. In this algorithm, the sensing results of secondary users are pre-filtered and applying fuzzy logic, so, the overall sensing performance of the network is improved. To determine pre-filter parameters, statistical parameters of the sensing results are used to remove those sensing results which are far from the majority sensing results. However, to obtain a better performance in the spectrum sensing, we propose a fuzzy logic to nullify the ef- fects of malicious users who transmit false sensing data to the fusion center. We further propose a Fuzzy Trust Level for each user as to weight the sensing result of the corresponding user before combining all sensing results in the fusion center. Simulation results demonstrate that our proposed algorithm yield signifi- cant improvement in the performance of the spectrum sensing and identifying malicious users. Keywords: Cognitive Radio, Cooperative Spectrum Sensing, Energy Detection, Malicious User Detection, Pre-filtering, Fuzzy Logic 1. Introduction Traditionally, fixed spectrum bands have been assigned to specific services for a long time. This policy has led to inefficient spectrum usage, and caused cognitive radio networks were proposed. In these networks, cognitive radios, which are called secondary (unlicensed) users are allowed to use the primary (licensed) users’ bands when such bands are unoccupied by primary users (Pus). However, the secondary users (SUs) must make the band vacant immediately after a PU starts transmitting in the corresponding band [1]. Therefore, the most important task of a cognitive radio is spectrum sensing. Spectrum sensing techniques include energy detection, cyclosta- tioary feature detection and matched filter detection [2-4]. The performance of a spectrum sensing is determined by two probabilities: probability of detection (Pd) and prob- ability of false alarm (Pf). Pd is the pro bability of declar- ing the chann el is occupied while the PU is present. Pf is the probability of declaring the channel is occupied by a PU while the PU has no transmission. Among different spectrum sensing schemes for reliably identifying the licensed spectrum status, the energy detector scheme incurs a very low implementation cost and therefore is widely used. It serves as the optimal method to detect the signal transmitted by a PU whose location is unknown, and the detector only knows the power of the received signal [6]. The problem of this scheme is that the re- ceived signal power can be seriously weakened at a par- ticular geographical location du e to multipath fading and shadowing effects [7]. In these circumstances, it is diffi- cult for a single sensing user to distinguish between an idle band and a deep faded one. In order to overcome this problem, cooperative spectrum sensing schemes have been proposed [5,8,9]. However, in cooperative sensing, due to imperfect channel between a primary user and a secondary user (SU) or dishonestly behavior of a SU, a user might send false sensing result to the fusion center. So, the performance of the system degrades severely. To overcome this problem, secure spectrum sensing has been proposed. In [8], a spectrum sensing data falsification problem was solved by weighted sequential probability ratio test (WSPRT), which gives a good performance. However, this method requires the knowledge of locations of sens- ing terminals and position of PU for obtaining some re- quired prior probabilities. This is inappropriate for mo- bile cognitive radios and for systems in which the loca- tion of the primary user is completely unknown. In [10], a robust secure distributed spectrum sensing scheme is  E. MOEENTAGHAVI ET AL. 508 proposed that uses robust statistics to approximate the distribution for both hypotheses of all users, discriminat- ingly, based on their past data report. Th e authors in [11] propose the majority rule in the fusion center to nullify the effects of the malicious users. In [5], an effective weighted combining method is proposed to reduce the impact of false information. In [12], a defense scheme is proposed that computes suspicious levels and trust values of the users. In our previous work [13], malicious user detection based on outlier energy detection techniques is proposed and a filtering method is used based on statis- tical parameters of sensing results to eliminate the effects of malicious users. In this paper, we propose a two step secure spectrum sensing algorithm. At first, based on the statistical parameters of SUs sensing results, a pre-filter is designed to remove the sensing results of the secon- dary users which are far from the others. Then, trust weighted values are assigned to the users whose sensing results are passed from the filter based on the fuzzy logic. Finally, a weighted combining method is proposed to make final decision in the fusion center. The rest of the paper is organized as follows: In Sec- tion 2, the system model is described and a brief back- ground about fuzzy logic is presented. In Section 3, our new algorithm to nullify the effects of malicious users is proposed. Simulation results are carried and analyzed in Section 4, and conclusions are drawn in Section 5. 2. System Description 2.1. System Model We discuss a cognitive radio network consist of one PU and a group of N SUs. A cooperative spectrum sensing is considered in which channels between a primary user and each secondary user have independent and identi- cally distributed (i.i.d) Rayleigh distributions. Variation in path-loss is neglected. Each SU conducts energy de- tection and transmits the measured value of received signal energy in a perfect (i.e. error free) control channel to the fusion center. By combining the sensing results received from different SUs, the fusion center makes the final decision regarding the presence or absence of the primary user. If en[k] for n=1,2, ···, N represents the re- ceived signal energy of nth SU at time instant k, hy- potheses H1 and H0 denote the presence and absence of the primary signal, respectively. Then, the signal energy received by nth SU is given by: 12 1 12 0 d, d, k k k k TT nn T nTT n T htstztt H ek zt tH (1) where T represents the time interv al of sensing, s(t) is the primary signal, hn(t) denotes the channel gain between the primary user and the nth secondary user, and zn(t) is the additive white Gaussian noise (AWGN). A threat to cooperative spectrum sensing is transmis- sion of false results by attackers to the fusion center, which leads to make a wrong decision (SSDF1 attack). So, cooperative spectrum sensing in adversarial envi- ronments where a malicious user sends false data de- grades the performance of the system severely. In adver- sarial environments, different kinds of malicious users can affect the spectrum sensing system. They may send data indicating the presence of the PU to the fusion cen- ter (“Always Yes” malicious users). These malicious users cause the fusion center to erroneously decide that the PU is present. Then, malicious users selfishly use the entire free spectrum band and also probability of false alarm is increased. Another kind of malicious are those who always send data indicating the absence of the pri- mary user (“Always No” malicious users). This kind of malicious users causes the interference among the pri- mary and secondary user’s signal and decrease probabil- ity of detection [14]. Therefore, the fusion scheme must be robust enough. In this paper, we propose a two step algorithm for secure spectrum sensing. In step 1, the sensing results in the data collector are pre-filtered and in step 2, we assign each user a Fuzzy Trust Level using fuzzy logic. In our proposed algorithm, more reliable users are assigned with higher trust levels. This algo- rithm also detects suspicious users with their corre- sponding suspiciou s levels using fuzzy logic. Finally, the sensing results are combined together based on their Fuzzy Trust Levels in the fusion center. 2.2. Overview of Fuzzy Logic In this section, we present a brief background on fuzzy logic. The reason for that is because our proposed algo- rithm integrates fuzzy logic with spectrum sensing in order to better detect malicious user. Fuzzy logic was introduced by Dr. Lotfi Zadeh of UC/Berkeley in the 1960’s as a mean to model the un- certainty of natural language. fuzzy logic, a widely de- ployed technology for developing sophisticated control systems [15,16], provides a simple way to get definite precise conclusion and solution based on unclear, impre- cise, ambiguous or missing input information. Figure 1 shows the steps that fuzzy logic controller is composed of. The steps of a fuzzy logic can be summarized as fol- lows: 1) receiving input values representing measure- ments of the parameters to be analyzed; 2) subj ecting the input value to if-then fuzzy rules; 3) averaging and 1Spectrum Sensing D ata Falsification Attack. Copyright © 2011 SciRes. IJCNS 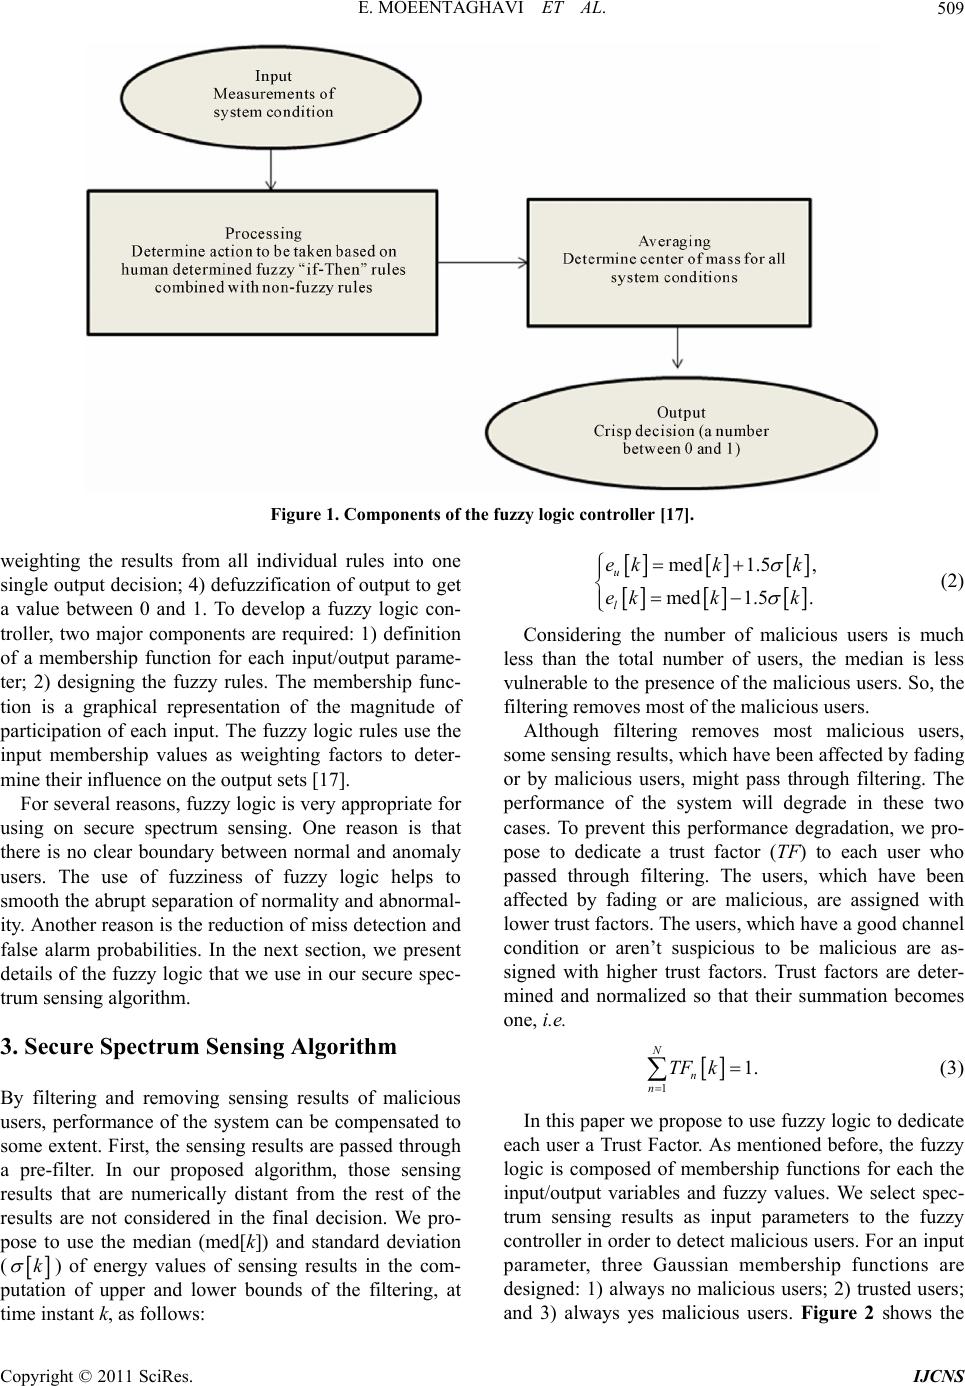 E. MOEENTAGHAVI ET AL. Copyright © 2011 SciRes. IJCNS 509 Figure 1. Components of the fuzzy logic controller [17]. med1.5 , med1.5 . u l ekk k ekk k (2) weighting the results from all individual rules into one single output decision; 4) defuzzification of output to get a value between 0 and 1. To develop a fuzzy logic con- troller, two major components are required: 1) definition of a membership function for each input/output parame- ter; 2) designing the fuzzy rules. The membership func- tion is a graphical representation of the magnitude of participation of each input. The fuzzy logic rules use the input membership values as weighting factors to deter- mine their influence on the output sets [17]. Considering the number of malicious users is much less than the total number of users, the median is less vulnerable to the presence of the malicious users. So, the filtering removes most of the malicious users. Although filtering removes most malicious users, some sensing results, which have been affected by fading or by malicious users, might pass through filtering. The performance of the system will degrade in these two cases. To prevent this performance degradation, we pro- pose to dedicate a trust factor (TF) to each user who passed through filtering. The users, which have been affected by fading or are malicious, are assigned with lower trust factors. The users, which have a good channel condition or aren’t suspicious to be malicious are as- signed with higher trust factors. Trust factors are deter- mined and normalized so that their summation becomes one, i.e. For several reasons, fuzzy logic is very appropriate for using on secure spectrum sensing. One reason is that there is no clear boundary between normal and anomaly users. The use of fuzziness of fuzzy logic helps to smooth the abrupt separation of normality and abnormal- ity. Another reason is the reduction of miss detection and false alarm probabilities. In the next section, we present details of the fuzzy logic that we use in our secure spec- trum sensing algorithm. 3. Secure Spectrum Sensing Algorithm 11. N n n TF k (3) By filtering and removing sensing results of malicious users, performance of the system can be compensated to some extent. First, the sensing results are passed through a pre-filter. In our proposed algorithm, those sensing results that are numerically distant from the rest of the results are not considered in the final decision. We pro- pose to use the median (med[k]) and standard deviation ( k ) of energy values of sensing results in the com- putation of upper and lower bounds of the filtering, at time instant k, as follows: In this paper we propose to use fuzzy logic to dedicate each user a Trust Factor. As mentioned before, the fuzzy logic is composed of membership functions for each the input/output variables and fuzzy values. We select spec- trum sensing results as input parameters to the fuzzy controller in order to detect maliciou s users. For an input parameter, three Gaussian membership functions are designed: 1) always no malicious users; 2) trusted users; and 3) always yes malicious users. Figure 2 shows the 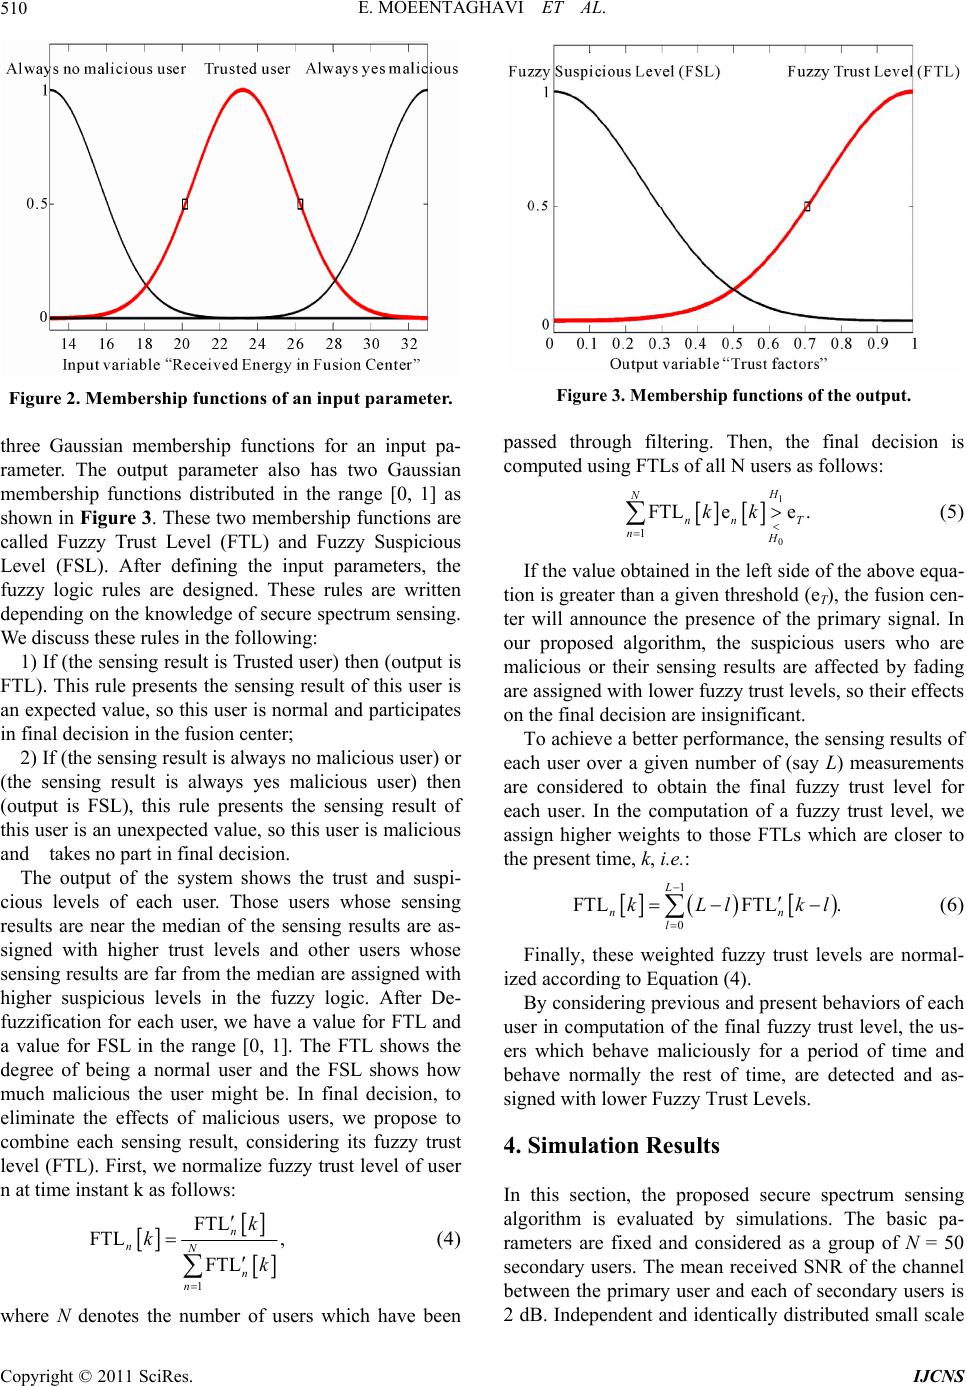 E. MOEENTAGHAVI ET AL. 510 Figure 2. Membership functions of an input parameter. three Gaussian membership functions for an input pa- rameter. The output parameter also has two Gaussian membership functions distributed in the range [0, 1] as shown in Figure 3. These two membership functions are called Fuzzy Trust Level (FTL) and Fuzzy Suspicious Level (FSL). After defining the input parameters, the fuzzy logic rules are designed. These rules are written depending on the knowledge of secure spectrum sensing. We discuss these rules in the following: 1) If (the sensing result is Trusted user) then (output is FTL). This rule presen ts the sensing result of this user is an expected value, so this user is normal and participates in final decision in the fusion center; 2) If (the sensing result is always no malicious user) or (the sensing result is always yes malicious user) then (output is FSL), this rule presents the sensing result of this user is an unexpected value, so th is user is malicious and takes no part in final decision. The output of the system shows the trust and suspi- cious levels of each user. Those users whose sensing results are near the median of the sensing results are as- signed with higher trust levels and other users whose sensing results are far from the median are assigned with higher suspicious levels in the fuzzy logic. After De- fuzzification for each user, we have a value for FTL and a value for FSL in the range [0, 1]. The FTL shows the degree of being a normal user and the FSL shows how much malicious the user might be. In final decision, to eliminate the effects of malicious users, we propose to combine each sensing result, considering its fuzzy trust level (FTL). First, we normalize fuzzy trust level of user n at time instant k as follows: 1 FTL FTL , FTL n nN n n k k k (4) where N denotes the number of users which have been Figure 3. Membership functions of the output. passed through filtering. Then, the final decision is computed using FTLs of all N users as follows: 1 0 1FTLee. H N nn T nH kk (5) If the value obtained in th e left side of the above equ a- tion is greater than a given threshold (eT), the fusion cen- ter will announce the presence of the primary signal. In our proposed algorithm, the suspicious users who are malicious or their sensing results are affected by fading are assigned with lower fuzzy trust levels, so their effects on the final decision are insignificant. To achieve a better performance, the sensing results of each user over a given number of (say L) measurements are considered to obtain the final fuzzy trust level for each user. In the computation of a fuzzy trust level, we assign higher weights to those FTLs which are closer to the present time, k, i.e.: 1 0 FTLFTL . L n l kLl k n l (6) Finally, these weighted fuzzy trust levels are normal- ized according to Equation (4). By considering previous and present behaviors of each user in computation of the final fuzzy trust level, the us- ers which behave maliciously for a period of time and behave normally the rest of time, are detected and as- signed with lower Fuzzy Trust Levels. 4. Simulation Results In this section, the proposed secure spectrum sensing algorithm is evaluated by simulations. The basic pa- rameters are fixed and considered as a group of N = 50 secondary users. The mean received SNR of the channel between the primary user and each of secondary users is 2 dB. Independent and identically distributed small scale Copyright © 2011 SciRes. IJCNS 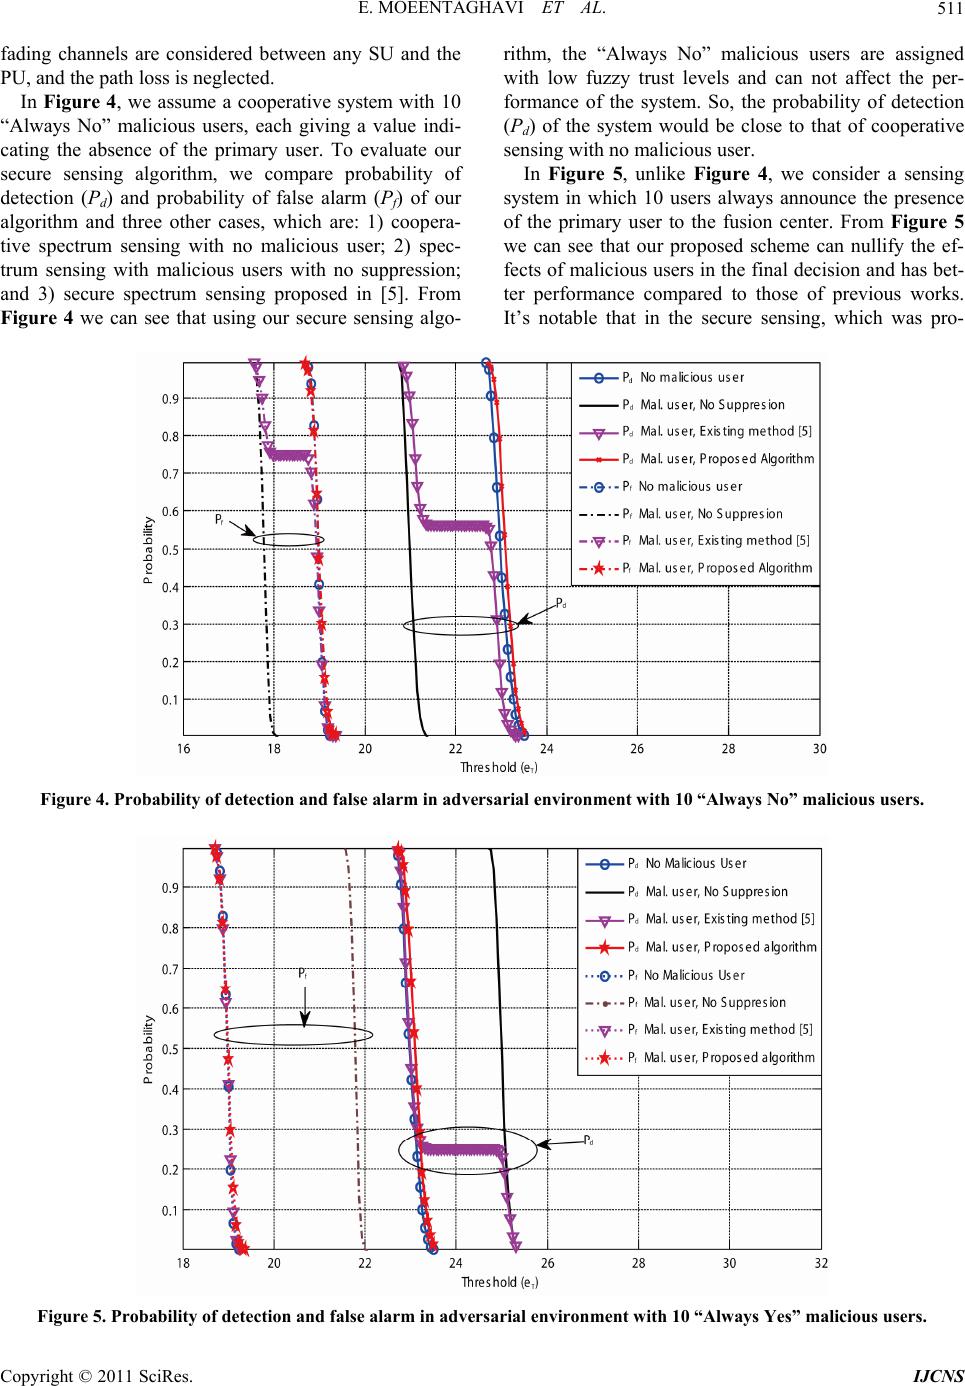 E. MOEENTAGHAVI ET AL. Copyright © 2011 SciRes. IJCNS 511 fading channels are considered between any SU and the PU, and the path loss is neglected. In Figure 4, we assume a cooperative system with 10 “Always No” malicious users, each giving a value indi- cating the absence of the primary user. To evaluate our secure sensing algorithm, we compare probability of detection (Pd) and probability of false alarm (Pf) of our algorithm and three other cases, which are: 1) coopera- tive spectrum sensing with no malicious user; 2) spec- trum sensing with malicious users with no suppression; and 3) secure spectrum sensing proposed in [5]. From Figure 4 we can see that using our secure sensing algo- rithm, the “Always No” malicious users are assigned with low fuzzy trust levels and can not affect the per- formance of the system. So, the probability of detection (Pd) of the system would be close to that of cooperative sensing with no malicious user. In Figure 5, unlike Figure 4, we consider a sensing system in which 10 users always announce the presence of the primary user to the fusion center. From Figure 5 we can see that our proposed scheme can nullify the ef- fects of malicious users in the final decision and has bet- ter performance compared to those of previous works. It’s notable that in the secure sensing, which was pro- Figure 4. Probability of detection and false alarm in adversarial environment with 10 “Always No” malicious users. Figure 5. Probability of detection and false alarm in adversarial environment with 10 “Always Yes” malicious users. 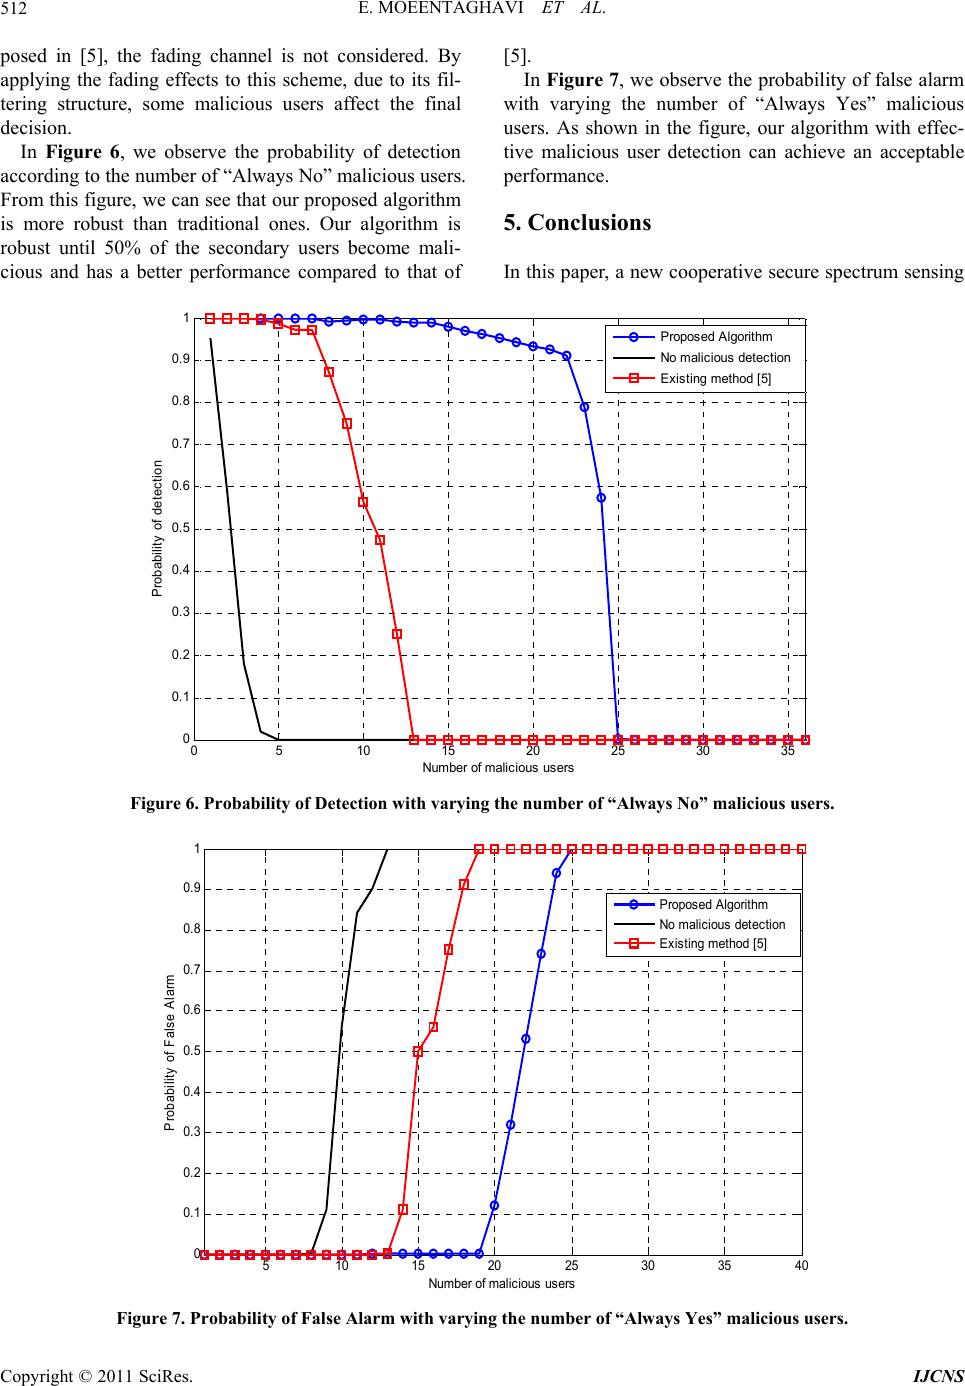 E. MOEENTAGHAVI ET AL. Copyright © 2011 SciRes. IJCNS 512 posed in [5], the fading channel is not considered. By applying the fading effects to this scheme, due to its fil- tering structure, some malicious users affect the final decision. In Figure 6, we observe the probability of detection according to the number of “Always No” malicious users. From this figure, we can see that our proposed algorithm is more robust than traditional ones. Our algorithm is robust until 50% of the secondary users become mali- cious and has a better performance compared to that of [5]. In Figure 7, we observe the probability of false alarm with varying the number of “Always Yes” malicious users. As shown in the figure, our algorithm with effec- tive malicious user detection can achieve an acceptable performance. 5. Conclusions In this paper, a new cooperative secure spectru m sensing 05 10 15 20 25 30 35 0 0.1 0.2 0.3 0.4 0.5 0.6 0.7 0.8 0.9 1 Number of mali ci ous users P robability of det ec t i on P roposed Al go rithm No malicious detection Existing method [5] Figure 6. Probability of Detection with varying the number of “Always No” malicious users. 510 15 2025 30 35 40 0 0.1 0.2 0.3 0.4 0.5 0.6 0.7 0.8 0.9 1 Number of mal ici ous users P robability of F als e A larm Proposed A l gorit hm No malicious detect ion Exis ti ng m ethod [5] Figure 7. Probability of False Alarm with varying the number of “Always Yes” malicious users. 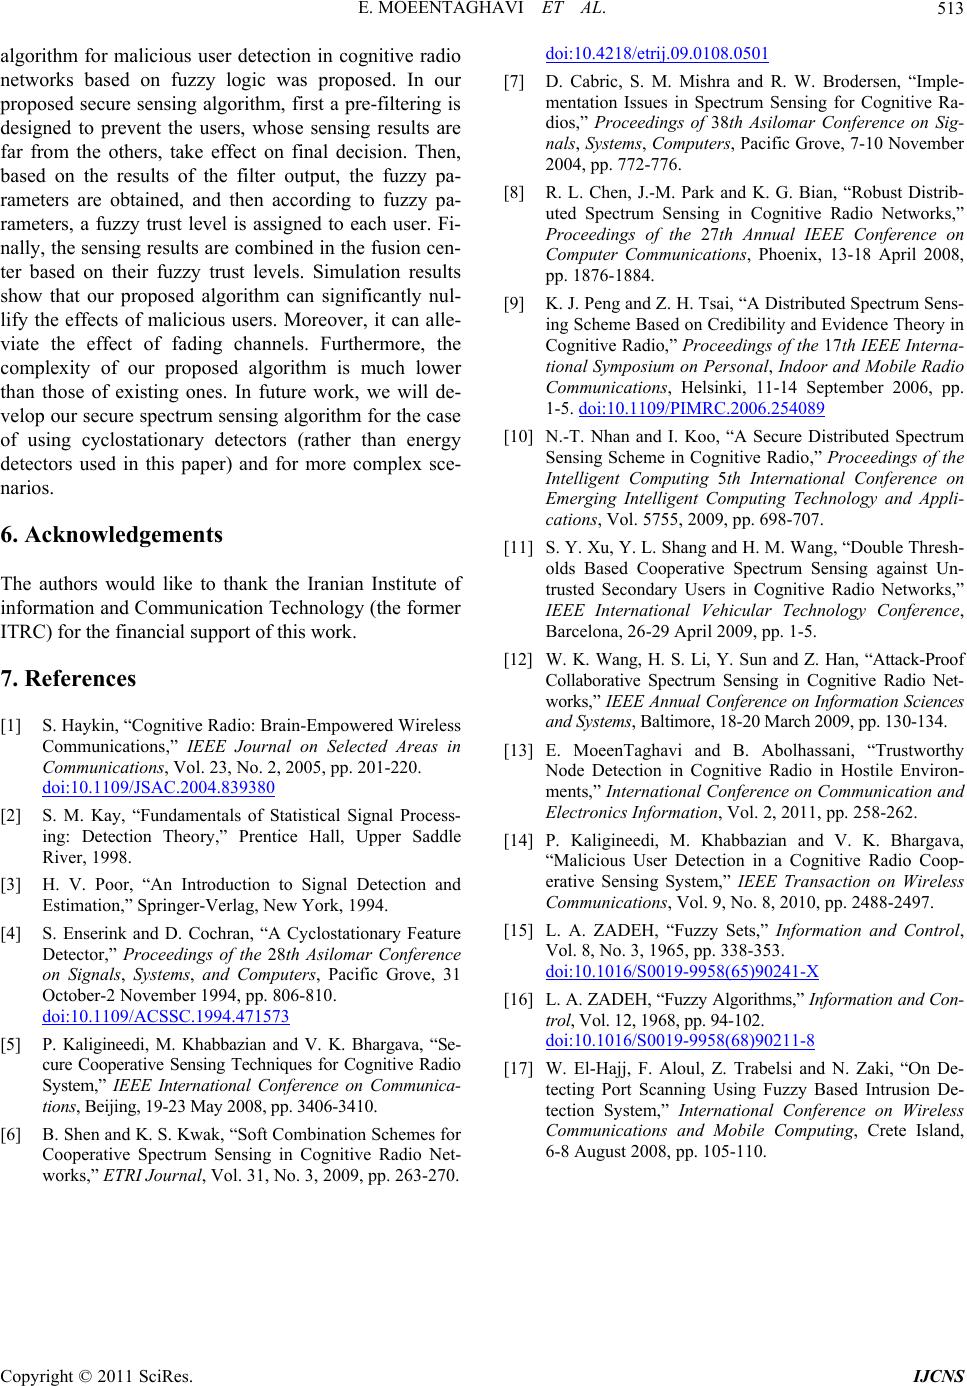 E. MOEENTAGHAVI ET AL. Copyright © 2011 SciRes. IJCNS 513 algorithm for malicious user detection in cognitive radio networks based on fuzzy logic was proposed. In our proposed secure sensing algorithm, first a pre-filtering is designed to prevent the users, whose sensing results are far from the others, take effect on final decision. Then, based on the results of the filter output, the fuzzy pa- rameters are obtained, and then according to fuzzy pa- rameters, a fuzzy trust level is assigned to each user. Fi- nally, the sensing results are combined in the fusion cen- ter based on their fuzzy trust levels. Simulation results show that our proposed algorithm can significantly nul- lify the effects of malicious users. Moreover, it can alle- viate the effect of fading channels. Furthermore, the complexity of our proposed algorithm is much lower than those of existing ones. In future work, we will de- velop our secure sp ectrum sensing algorithm for the case of using cyclostationary detectors (rather than energy detectors used in this paper) and for more complex sce- narios. 6. Acknowledgements The authors would like to thank the Iranian Institute of information and Co mmunication Technology (th e former ITRC) for the financial support of this work. 7. References [1] S. Haykin, “Cognitive Radio: Brain-Empowered Wireless Communications,” IEEE Journal on Selected Areas in Communications, Vol. 23, No. 2, 2005, pp. 201-220. doi:10.1109/JSAC.2004.839380 [2] S. M. Kay, “Fundamentals of Statistical Signal Process- ing: Detection Theory,” Prentice Hall, Upper Saddle River, 1998. [3] H. V. Poor, “An Introduction to Signal Detection and Estimation,” Springer-Verlag, New York, 1994. [4] S. Enserink and D. Cochran, “A Cyclostationary Feature Detector,” Proceedings of the 28th Asilomar Conference on Signals, Systems, and Computers, Pacific Grove, 31 October-2 November 1994, pp. 806-810. doi:10.1109/ACSSC.1994.471573 [5] P. Kaligineedi, M. Khabbazian and V. K. Bhargava, “Se- cure Cooperative Sensing Techniques for Cognitive Radio System,” IEEE International Conference on Communica- tions, Beijing, 19-23 May 2008, pp. 3406-3410. [6] B. Shen and K. S. Kwak, “Soft Combination Schemes for Cooperative Spectrum Sensing in Cognitive Radio Net- works,” ETRI Journal, Vol. 31, No. 3, 2009, pp. 263-270. doi:10.4218/etrij.09.0108.0501 [7] D. Cabric, S. M. Mishra and R. W. Brodersen, “Imple- mentation Issues in Spectrum Sensing for Cognitive Ra- dios,” Proceedings of 38th Asilomar Conference on Sig- nals, Systems, Computers, Pacific Grove, 7-10 November 2004, pp. 772-776. [8] R. L. Chen, J.-M. Park and K. G. Bian, “Robust Distrib- uted Spectrum Sensing in Cognitive Radio Networks,” Proceedings of the 27th Annual IEEE Conference on Computer Communications, Phoenix, 13-18 April 2008, pp. 1876-1884. [9] K. J. Peng and Z. H. Tsai, “A Distributed Spectrum Sens- ing Scheme Based on Credibility and Evidence Theory in Cognitive Radio,” Proceedings of the 17th IEEE Interna- tional Symposium on Personal, Indoor and Mobile Radio Communications, Helsinki, 11-14 September 2006, pp. 1-5. doi:10.1109/PIMRC.2006.254089 [10] N.-T. Nhan and I. Koo, “A Secure Distributed Spectrum Sensing Scheme in Cognitive Radio,” Proceedings of the Intelligent Computing 5th International Conference on Emerging Intelligent Computing Technology and Appli- cations, Vol. 5755, 2009, pp. 698-707. [11] S. Y. Xu, Y. L. Shang and H. M. Wang, “Double Thresh- olds Based Cooperative Spectrum Sensing against Un- trusted Secondary Users in Cognitive Radio Networks,” IEEE International Vehicular Technology Conference, Barcelona, 26-29 April 2009, pp. 1-5. [12] W. K. Wang, H. S. Li, Y. Sun and Z. Han, “Attack-Proof Collaborative Spectrum Sensing in Cognitive Radio Net- works,” IEEE Annual Conference on Information Sciences and Systems, Baltimore, 18-20 March 2009, pp. 130-134. [13] E. MoeenTaghavi and B. Abolhassani, “Trustworthy Node Detection in Cognitive Radio in Hostile Environ- ments,” International Conference on Communication and Electronics Information, Vol. 2, 2011, pp. 258-262. [14] P. Kaligineedi, M. Khabbazian and V. K. Bhargava, “Malicious User Detection in a Cognitive Radio Coop- erative Sensing System,” IEEE Transaction on Wireless Communications, Vol. 9, No. 8, 2010, pp. 2488-2497. [15] L. A. ZADEH, “Fuzzy Sets,” Information and Control, Vol. 8, No. 3, 1965, pp. 338-353. doi:10.1016/S0019-9958(65)90241-X [16] L. A. ZADEH, “Fuzzy Algorith ms,” Information a nd Con- trol, Vol. 12, 1968, pp. 94-102. doi:10.1016/S0019-9958(68)90211-8 [17] W. El-Hajj, F. Aloul, Z. Trabelsi and N. Zaki, “On De- tecting Port Scanning Using Fuzzy Based Intrusion De- tection System,” International Conference on Wireless Communications and Mobile Computing, Crete Island, 6-8 August 2008, pp. 105-110. |